Discover and govern
your AI agents
Guardian Agent gives your teams visibility and policy control across AI agents, enterprise tools and the systems they access.
Know what your agents can access
Find unmanaged agents
Bring human and agent activity across approved and shadow AI into view.
Review access and behavior
Assess tools, permissions and runtime actions before agent risk spreads.
Policy control across the agent lifecycle
Explore how Guardian Agent helps teams discover, assess and control AI activity across enterprise environments.
Agent Discovery & Inventory
Discover AI agents across your environment and bring their identities, access and activity into a governed view.
Connector Catalog
Organize the enterprise tools and integrations available to agents, with a clear record of approved connections.
Agent Map
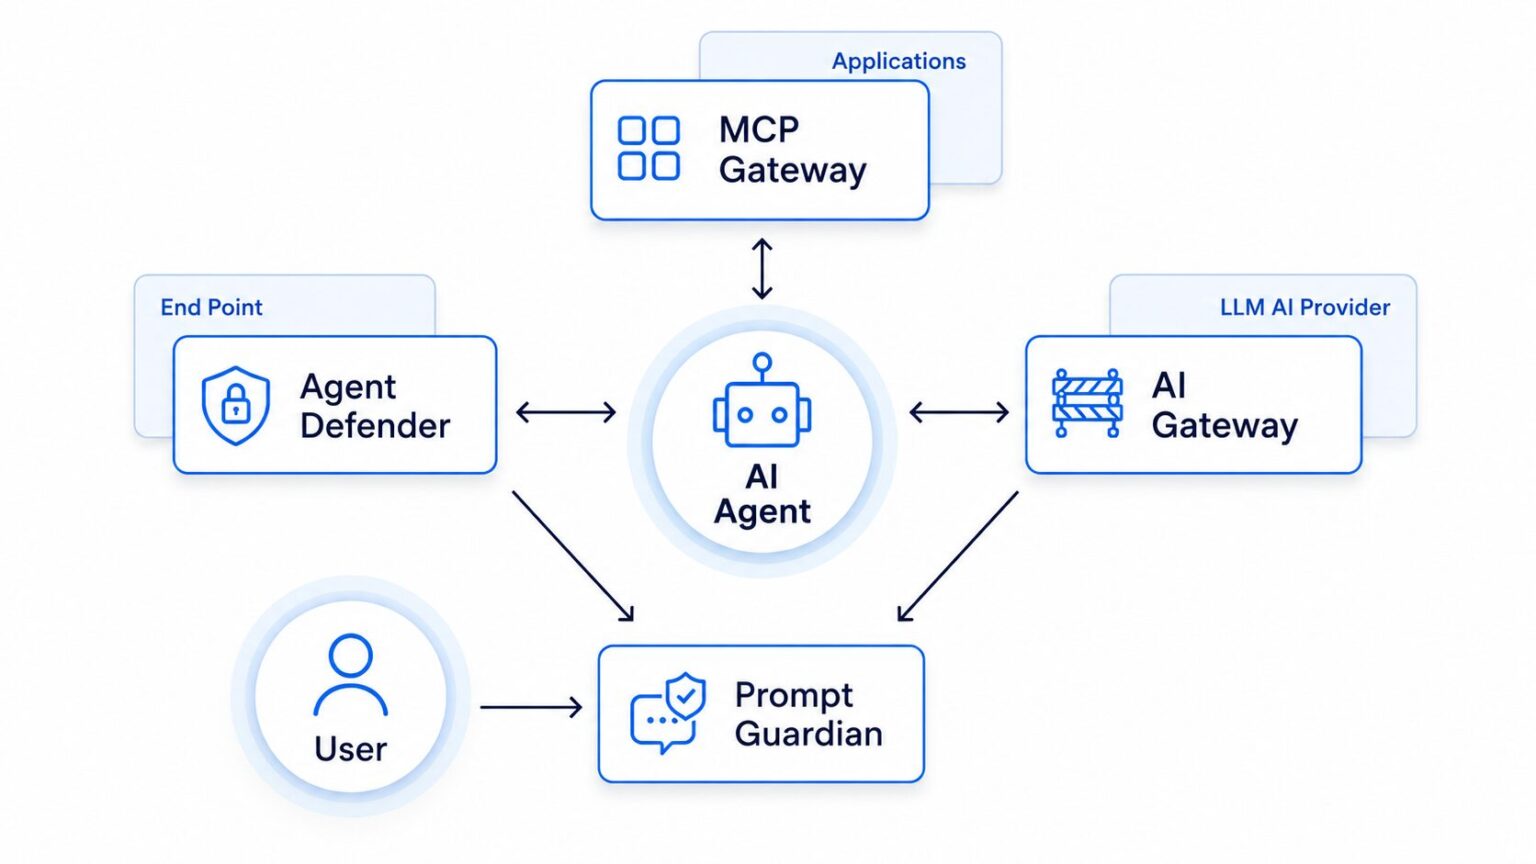
Understand how agents connect to applications, MCP tools and data so security teams can review their reach.
Agent Policy Engine
Apply organization policies to agent activity and define which actions can proceed, be blocked or require review.
MCP & Tool Governance
Control access to enterprise resources through the MCP Gateway and enforce tool permissions at runtime.
Agent Identity & Access Control
Manage agent identities and access boundaries so tools and data are available only within approved permissions.
Monitoring & Traceability
Follow agent activity across tools and workflows, with the evidence needed for investigation and governance.
Runtime Action Enforcement
Assess actions as they happen and stop operations that fall outside the organization’s security policy.
Agent Defender
Extend visibility and policy enforcement to endpoint agents and coding assistants, including tools beyond MCP.
Shadow AI Agent Detection
Identify unmanaged AI activity across the enterprise and bring previously unknown agents into security review.
Enable agents with security built in
Monitor activity.
Control the risk.
See how agents interact with your environment and apply governance where work happens. Build an evidence-based approach to adopting AI safely.
- Visibility across cloud, SaaS, endpoints and developer tools
- Policies for tools, data and agent actions
- Traceability for security and governance teams
Broader visibility
Understand AI use across enterprise applications, endpoints and developer environments.
Controlled access
Define how agents connect to business tools, enterprise resources and data.
Reviewable activity
Support investigation and governance with monitoring and traceability.
Safer adoption
Support useful AI workflows while applying policy to risky activity.
Years of Compliance Expertise
Enterprise Deployments
Companies Trust Us
Put agent governance
into practice
Discuss your AI environment, policy needs and deployment options with the Promshield team.